QA Consulting and Software Quality Audit whose findings you own, whoever closes them.
A software quality audit is an outside read on how a company builds quality into its software: what actually gets tested, what nobody is watching, and which of those gaps would cost real money.
- 120+Projects delivered across 12 countries since 2012
- 100+Senior in-house engineers, six countries
- 5.0Unified rating across 61 client reviews on Clutch
- ISTQBCertified QA inside every sprint
- ISO 9001Certified quality management, audited by Quay Audit UK
01Overview
What a unicrew quality audit gives you
unicrew reads your quality practice from outside it and hands the read back. Test strategy, coverage, automation and release gates, assessed against what your tracker, your pipeline and your release records actually show. You leave with every gap ranked by risk against effort, and a roadmap your own team can execute.
- The read does not commit you to the fixBuying the audit and stopping there is a complete purchase. Whether we close any of the findings is a separate decision.
- The bar is your risk, not our scorecardA finding is high-risk when the failure would cost your business, and that call is yours. We rank on it and show the working, so the order of the fixes is something you can argue with.
- Read-only access, under NDANDA before any access. For the assessments and audits we work from read-only, least-privilege access, agreed with your technical contact before anything starts.
- When testing is the next stepFull-cycle QA if you want the testing run, test automation if the suites are the gap, and AI QA and evals if the untested surface is a model.
02Proof
Audits we ran, and audits of our own work
Booked It had a third party audit the code we wrote. Cloud Van Lines had outside experts assess our work for commercial viability. An auditor that has never been audited is asking for trust it has not earned.
- Open Room Inc. hired an impartial readTheir Forest real estate platform in Japan was developed in-house, with the QA brought in from outside the build team. We explored the product ourselves, then built the QA workflow, a tailored Test Cases System, TestCafe automation and a Testing Roadmap their own team runs.Less timeto release, in their CTO's words: "our releases took less time and were less stressful"
- Code we wrote, read by somebody elseBooked It's CEO Brad Nobbs: "We have had the code audited by a 3rd party who was extremely complimentary of the work." Cloud Van Lines' CEO Jeff Chizmas: "I had some other experts assess their work to see if the product was commercially viable, and everyone was impressed by the quality of the product." Both commissioned the read themselves.600+businesses running on the booking platform whose code that third party read
- Coverage checked across a seven-market switchoverJewelCandle moved seven national shops onto Shopify with a Microsoft Dynamics ERP and custom middleware behind them. Automated, load and stress testing ran through the whole build while the system was still changing, and the Test Plan and Test Cases behind it stayed with their team.10,000-plusproducts manufactured, sold across seven EU countries
03Compare
In-house review, an outside audit, or nothing yet?
Pick by whether anyone left inside your organization can still see the process from outside it. Two answers sit outside the table: full technical due diligence, which is wider and shallower on testing and runs to an investor's timetable (technology advisory covers it), and timing: an audit pays back most from product-market fit onwards, and waiting gets expensive after that point.
| An independent auditunicrew | Reviewing yourselvesInternal | A tool-led assessmentScan |
|---|---|---|
| Best forYou want an impartial read on how quality is built in, from people with no stake in defending the current setup. | Best forSmall teams where the tester, the developer and the person who owns the release still see the whole picture. | Best forA fast, cheap baseline number on coverage, static analysis findings or known vulnerabilities. |
| Works best withA question you cannot yet answer from inside, and a team ready to run the plan that comes back. | Works best withReviewers who can step outside their own assumptions, and roadmap time protected for the review every sprint. | Works best withA strategy around the number, and someone to judge whether the covered paths are the ones that would cost you money. |
| You end up owningThe findings, the ranking behind them, and a roadmap your own team can run. | You end up owningA view nobody outside the team that wrote the code has argued with. | You end up owningA dashboard, and the job of deciding what its number means. |
Quick self-check
Tick what is true for you. The read-out updates as you go.
0 of 4 true
Go straight to the fix
Your team can already name its coverage, read a defect trend off the tracker and say what gates a release, which is most of what an audit reports back. The next step is the fix: test automation if the suites are the gap, a full-cycle QA team if the testing is.
Talk it throughScope it down to the one path
One tick points at a path, not at a system. Reading one product or one release path is a far smaller commitment than reading everything, and it answers the question you actually have.
Talk it throughThe document and the evidence have drifted
Two ticks is the shape of a practice that has moved away from what it says it does. Nobody inside the drift can measure it, which is what the assessment stage exists to surface.
Book a discovery callThe question is no longer whether, but how wide
Three ticks, and what is left to settle is which products, which teams, and whether the answer goes to a board or to a QA lead. Those are not the same document.
Book a discovery callBuy the read, and budget for the fix
All four describe an organization that cannot answer a question about itself from the inside, with somebody outside about to ask it. Budget for closing the findings, not only for receiving them.
Start with scopeWe write every audit finding so your own team can act on it. Each one is specific enough for your engineers to start on the next day, whether they close it or we do.
 Ihor PrudyvusDelivery Director, unicrew
04Capabilities
What a quality audit examines
Eight dimensions, and the same question in each: how does quality get built in here, and where would it fail without anyone noticing? This is a read on the system that produces your software rather than a line-by-line review of the code.
- Test coverage assessment
Test strategy and coverage
Risk against what is testedWe map what is tested against what would hurt if it broke. Coverage percentage is the input; the finding is which critical path has nobody watching it.
- Test automation assessment
Test automation readiness
What to automate nextWe assess the suite you have and what it costs to keep green. Sometimes the honest answer is that a flaky suite nobody trusts should be deleted rather than extended.
- Release process audit
Release gates and CI/CD discipline
Version control and deploymentWe look at what has to be true before code reaches your users, and how often that gate gets waived. On one live SaaS platform, version control and deployment automation took a multi-week release down to hours.
- Performance and load test review
Performance and load coverage
Under real trafficWe check whether your performance and load testing covers the scenarios that matter, and when each pass last ran. Passing at last year's traffic shape is not evidence about this year's.
- Security process review
Security and compliance checks
Claimed, or actually checkedWe review how security is verified inside your process and flag where a standard you claim to meet is not actually being checked. On a legal-industry SaaS that meant encryption at rest and in transit, no administrator access to user data, and the OWASP standards followed. An adversarial engagement is a separate service.
- User-facing test coverage
Usability and accessibility coverage
Design problem or defectWe review whether user-facing quality gets tested at all, or only assumed. Where what we find is a design fault instead of a defect, UX consulting and audit owns it: heuristic evaluation, independent user testing and WCAG review, as a product of its own.
- AI and LLM test coverage audit
AI feature evaluation
Output is not deterministicIf your product ships LLM or agent features, your existing suite almost certainly does not cover them, because the output is not deterministic. We flag that gap and what an evaluation harness would need.
- Defect management audit
Defect management and QA documentation
Found, triaged, owned, closedWe look at how defects are found, triaged, owned and closed, and whether any of it is written down. On a platform where we run the QA ourselves, that meant a workflow where every bug starts from a triggering event and gets assigned to an owner, with structured QA documentation behind it.
05Trust
What you walk away with
You keep all three of these whether or not we ever touch the fix: the scored gaps, the roadmap behind them, and a re-audit against the same findings if you want one.
- RankedEvery gap scored on risk against effortso a finding you disagree with can be argued on its evidence
- Yours to runA prioritized QA roadmapwritten for your own team to execute, not written to require us
- Re-auditThe same findings checked after the changes shipoptional, and the only honest way to know a gap closed rather than moved
06Stack
The stacks and tools an audit reads
We audit in whatever you already run. Tooling is the smallest part of a finding: a green suite tells you it ran, not whether it covered the paths that would cost you money.
 JavaScript
 TypeScript
 PHP
 Yii2
 Laravel
 MySQL
 AWS
 Shopify
- Microsoft Dynamics
 TestCafe
07Engagement
How you engage us on an audit
Three shapes, and the first is the product: a read and a roadmap, with any delivery afterwards left as your decision. Which one fits is something we settle on the first call, not something you have to pick now.
The audit, then it is yours
Report onlyThe full read: scope, assessment, ranked findings, roadmap, handover. Stopping there is a complete purchase. There is no minimum engagement period.
- Best when
- You need an outside read on the whole quality system
- You pay
- Outcome based, quoted per project
- Typical start
- Two to four weeks
A focused read on one path
Single pathOne product, one team or one release path. Smaller than a full audit, and the right shape when a single gap is already obvious.
- Best when
- The question is one release path, not the whole organization
- You pay
- Billed hourly, quoted per project
- Typical start
- Two to four weeks
The audit, then the fix with us
Then deliveryIf you would rather not run the roadmap yourself, the people who wrote the findings can close them, as a named team inside your process.
- Best when
- You want the findings closed by the people who wrote them
- You pay
- Billed monthly, per team member
- Typical start
- Two to four weeks
A re-audit is a different job from a first read
An audit that already exists and never moved does not need a second opinion on the same scope. The question is which findings closed, which moved, and which were never funded. That is a re-audit: short, because it checks the same findings against the same evidence. If you already know the gap, go straight to the fix.
08Industries
The domains behind this work
A payment path, a multi-market catalogue and a real estate deal flow each fail differently, and an audit that does not know the domain grades the test suite while missing the risk. These six are where the work has been.
Logistics and transportation
Dispatch, warehouse and fleet systems that have to keep running while the business does, from an order management platform for a household-moving company to finished-vehicle logistics. A bad release here stops the operation rather than annoying a user.
Hospitality and leisure
Venue, membership and ticketing platforms whose worst week to be wrong is also their busiest. The booking platform we refactored was later read by a third party the client hired themselves.
Real estate
We are the independent QA provider on a Japanese real estate platform, where the client's own developers build the product and we run the QA alongside them.
E-commerce
Automation, load and stress testing behind a seven-market re-platforming onto Shopify, with a Microsoft Dynamics ERP and custom middleware behind it.
Financial services
Accessibility compliance and technical QA were both in scope across four corporate sites for a financial services group, whose own bar was that quality must not drift from one site to the next.
Healthcare
A regulated vertical where a defect is a compliance event rather than a bug. We stabilized a home health monitoring platform to the point of minimal end-user support requests.
Send us what you already test, and we will show you whether an audit would add to it
Thirty minutes on what you ship and what breaks. You will come out of it knowing what an audit would cover on your product, what it would leave alone, and what it would need from your team.
What happens after you contact us
- We reply within one business dayThe reply names the questions an audit would answer about what you described.
- A call about what you ship and what you already testWhich products, teams and repositories are in scope, and what you want the audit to answer.
- A written audit scope, before anything startsThe question it answers, the access list behind it, and read-only access agreed under NDA.
- You decide, with no pressureThe scope is yours to accept, change or walk away from. Most engagements start within two to four weeks.
09Delivery
How a QA audit works
Five stages: scope and access, assessment, analysis and prioritization, findings and roadmap, handover. What sets the calendar is access rather than analysis, which is why every stage below names what we need from you.
- Scope and accessWe agree what is in scope and what question you want answered, because an audit for a board is not the same document as one for a QA lead. From you we need read access to the code, the tracker and the pipeline.You getA written audit scope, the question it answers, and the access list.
- Assessment of how you test todayWe review the practice against evidence rather than the process diagram: test cases, defect history, pipeline runs, release records, and what people do when a deadline is close. From you we need a couple of hours from whoever knows releases best.You getA written picture of how testing actually runs today, with the strengths named as well as the gaps.
- Analysis and prioritizationWe rank every gap by risk and by the effort to close it, and show the reasoning behind the order instead of asking you to take it on trust. From you we need a read on which failures actually cost money: that part is a business judgment.You getA risk-and-effort ranking of every finding, with the reasoning behind each position.
- Findings and roadmapThe roadmap is sequenced so the first weeks reduce the most risk: what to automate first, what to leave manual, what to gate a release on, and what has to be written down for the process to survive people leaving. From you we need your release calendar and anything already committed, so the sequence fits around what you have promised.You getA prioritized QA roadmap, plus the automation and manual split behind it.
- Handover and re-auditWe walk your team through the plan so they can act on it without us. From you we need the people who will do the work in the room, not only whoever commissioned the audit.You getA working session, and an optional re-audit against the same findings after the changes ship.
10Client voices
Our clients say
Our platform has been refactored to Laravel ensuring the code base is more stable, easier to maintain and easier to add new features. Their professionalism and quality of work have stood out in the partnership. We have had the code audited by a 3rd party who was extremely complimentary of the work.
Artelogic’s work had a very positive impact on our team’s morale. As our development quality was improving, our engineers were more confident in what they were doing, allowing them to work faster and with more confidence. As a result, our releases took less time and were less stressful.
They’re a highly ethical and well-managed organization. I was amazed by the CEO’s skill level and business acumen.
We were able to get the work completed in the expected time frame. There were little to no defects which was very nice because it allowed us to release and move on to our next project without having to back peddle. They were very accessible and took the time to understand our needs. They truly felt like part of the team.
We have had six out of seven on time and on budget project executions. Each engagement was a minimum of six months of effort. They had a flexibility and willingness to adapt their processes to match my requirements both on communication and the development processes. I never had a problem with any of their code from a code quality perspective.
11Case studies
Our case studies
One quotation above names Artelogic, which is what unicrew was called from 2012 until the rebrand; client reviews are reproduced as the clients wrote them. The three studies below are the ones where testing and release discipline are the visible part of the story.
See all case studies SaaSWaiverKing: Software Development for Waiver Form CreatorWaiverKing is a document management business serving primarily the health and fitness industries. The platform is partnered with MindBody Online, one of the largest business-systems providers for gyms and yoga studios.Weeks to hoursTime for an update to reach live
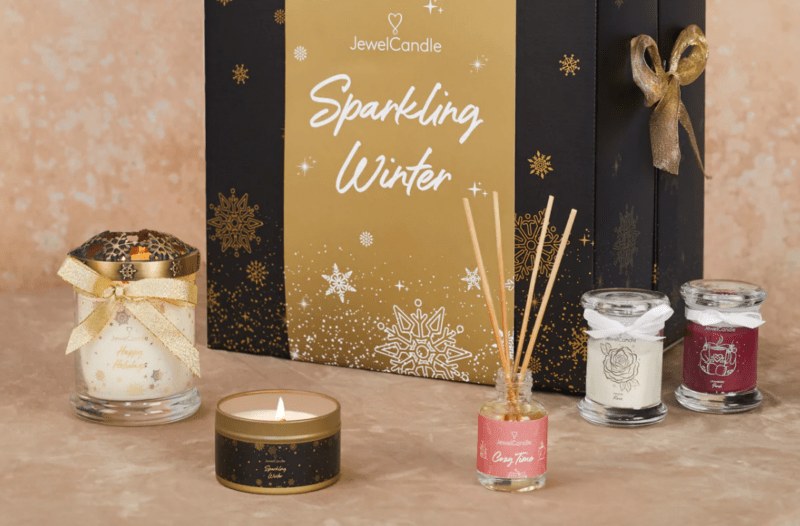 eCommerceEcommerce software development for JewelCandleJewelCandle, a mid-size European manufacturer of scented products, sells across seven EU countries (B2B and B2C) via online shops.10,000-plusProducts manufactured
 HospitalityHighly Adjustable Platform for entertainment industriesunicrew developed a platform for Booked It that enhanced the customer experience for nightclub, entertainment center, and festival goers.600+Businesses using the platform
12Questions
More about quality consulting and audit with unicrew
A findings report and a roadmap, then a working session where we walk your team through both. The report covers workflow, coverage, automation readiness and release gates, every gap ranked by risk against effort with the reasoning shown, so you can see why each fix sits where it does. The roadmap is written for your own team to execute. Where an engagement goes further than the read, we build the artifacts too: on an independent QA engagement for a real estate platform, an impartial analysis of the client's QA roadmap turned into a QA workflow, a tailored Test Cases System, automation on top of it, and a Testing Roadmap their own team applies at every stage.
Against the evidence, and against your own risk. We take what your process says happens and check it against what your tracker, your pipelines, your test cases and your release records actually show, because that gap is the one thing the people inside it cannot measure. Ranking is the second half. A finding is high-risk when the failure behind it would cost your business real money, and that judgment is yours: we bring the evidence and the reasoning for each position, and you can move a finding up or down knowing what it costs. There is no maturity score we sell you and no scale you are graded on.
QA consulting and a software quality audit are the same purchase here: an independent assessment of how you build quality in, ranked findings and a roadmap. Buyers search for it as quality assurance consulting, QA consulting services, software quality consulting and QA audit services, and all of those land on this page. QA services is a different purchase: somebody running the testing for you, release after release. That is full-cycle software testing and QA. If the strategy is fine and the suites are the bottleneck, it is QA and test automation.
The number follows the reading, because the same audit costs different money depending on how much there is to read. What moves it: how many products, teams and repositories are in scope, how much automation already exists, and whether the answer has to hold up in a data room. A full read is quoted per project, outcome based. A focused read on one path is billed hourly, quoted per project. If it turns into ongoing delivery, that is team extension, billed monthly per team member. You see the number before you commit, and there is no minimum engagement period.
The duration depends on what already exists. One product with written acceptance criteria, a staging environment and a test-case repository moves far faster than a multi-team estate where the coverage lives in people's heads. You hear about the risky gaps as we find them, before the report is finished. Scope and schedule are agreed before the audit starts.
No, and that would defeat the point: the audit is about your setup, not a recommended one. We read your tracker, your CI pipelines, your test repositories and your release process where they sit, and a finding that starts with "first migrate to" is one we have to justify twice. On one live SaaS platform the fix was version control in Git plus deployment automation alongside the test suite, which took release time from weeks to hours. On a seven-market e-commerce re-platforming it meant testing across Shopify, a Microsoft Dynamics ERP and the middleware between them, because the defects that hurt live between systems rather than inside one.
Four situations, all the same shape: somebody outside is about to ask a question. A business platform after a legacy refactor, where you need evidence the rebuild is stable and performs. A company going for ISO certification, where the QA process and its documentation have to hold up under examination. A company approaching an M&A, where the audit protects the software going into diligence; if you need the wider technical read rather than the quality one, that is technology consulting and advisory. And a startup at exit stage, where a buyer will examine your codebase whether or not you have. The cheapest time to find a coverage gap is before somebody else finds it: an audit six months before a data room is a cheap fix, while the same findings surfaced by the buyer's diligence team are a price negotiation.
Yes, we get you ready for the audit, and the certificate itself comes from an accredited body, as does a signed conformity assessment against a safety-critical standard such as IEC 62304 or DO-178C. unicrew holds ISO 27001:2022 and ISO 9001:2015 itself, renewed through a multi-stage audit with Quay Audit UK, so the standard we audit you against is one we live under. Our QA engineers are ISTQB certified.
Whatever you run, plus the classes of tooling a mature setup usually has. Test automation: TestCafe, Selenium, JUnit, TestNG. Performance: JMeter, LoadRunner. Security: OWASP ZAP, Burp Suite. CI and deployment: Jenkins, GitLab CI. Manual: exploratory testing, with test case management in TestRail. Usability: UsabilityHub, UserTesting, and the Nielsen heuristics method. We are not tied to any of them. On a platform where we owned the QA we built the automation on TestCafe, which runs browser tests in JavaScript or TypeScript across multiple browsers.
Three checks separate an audit you can act on from a report you file, and we answer all three. Ask what one finding actually looks like: a rank, the evidence behind it and the reasoning that put it there is something you can argue with, where a severity label on its own is not. Ask what the assessor's own certification covers, because judgment is the thing you are buying: ours is ISO 27001:2022 and ISO 9001:2015, renewed through a multi-stage audit with Quay Audit UK, and our QA engineers are ISTQB certified. And ask whether the people writing the findings are in-house, which decides whether whoever ranked your gaps is still there for the re-audit: ours come from 100+ senior in-house engineers across six countries. Every client quoted on this page links to their own Clutch review below, so you can read each interview in full.
Yes, whenever you want us to, as a separate decision from the audit. The engagement ends with a plan your own team can execute, and running it yourselves is the outcome we design for. If you do want help afterwards, it is full-cycle software testing and QA, QA and test automation or AI QA and LLM evaluation, depending on which surface is untested. If you would rather we simply confirm the work landed, we re-audit after it ships.