Industry software development
Domain depth, not just code. unicrew builds and runs operational software and AI for companies in logistics, travel, fintech, healthcare, commerce, energy, automotive, proptech and education. Every page below names what we build in that sector, the integrations involved, and the work we have published.
An ISO 27001:2022 certified security posture, ISO 9001:2015 quality management, both audited by Quay Audit UK, and ISTQB-certified QA.
- 120+Projects delivered across 12 countries since 2012
- 100+Senior in-house engineers, six countries
- 5.0Unified rating across 61 client reviews on Clutch
- ISTQBCertified QA inside every sprint
- ISO 27001Certified security practice, audited by Quay Audit UK
01Directory
Every industry we serve, and what we build in it
Domain knowledge, not just code: 9 industries, plus 7 specialized platform builds that sit inside them. Every card names what we build there and where to go deeper, and our three priority sectors lead, with the rest ordered by how many published case studies sit behind them. Search it if you already know the system you need.
Industries we serve
Transportation & Logistics
TMS, WMS, dispatch and last-mile software, integrated with your carriers, plus voice AI for operations.
4 published case studiesA freight-management platform and mobile apps for a US logistics startup (Mover Technologies)
Financial Services & Fintech
Payments, ledgers, reconciliation, KYC and AML flows, built by an ISO 27001:2022 certified team.
Go deeper
2 published case studiesFour corporate websites for a financial-services group, with accessibility inside the build scope
Healthcare
Clinical and patient workflows built to HIPAA Security Rules, with HL7 and FHIR integration.
2 published case studiesStabilizing and Scaling a Home Health Monitoring Platform
Hospitality & Travel
Booking, guest experience, and conversation intelligence. A decade of travel tech.
4 published case studiesA salon booking platform doing 200-300 bookings per vendor a month (Lookgood)
LMS & EdTech
Full-cycle learning management and EdTech platform development.
3 published case studiesThe custom time-tracking tool that got around 40% more project leaders tracking time at RWTH Aachen University
Automotive
AI-driven software for vehicle services, dealer operations, and connected mobility.
2 published case studiesService Intelligence: App for vehicle maintenance
Retail & E-commerce
Custom commerce, personalization, and agent-ready workflows.
Go deeper
1 published case studyEcommerce software development for JewelCandle
Real Estate & PropTech
Listing platforms, property management, MLS and RETS integrations, and AI features.
1 published case studyQuality Assurance service for Japanese real estate platform
Energy & Utilities
Custom software and AI for energy and utilities operators.
Go deeper
1 published case studySoftware for trading with Smart contracts
Specialized platform builds (7)
Systems clients ask for by name. Each sits inside one of the industries above.
Logistics ERP
Enterprise resource planning tuned for logistics and supply chain operations.
Part of
4 published case studiesA freight-management platform and mobile apps for a US logistics startup (Mover Technologies)
Warehouse Management
WMS platforms, inventory and fulfillment APIs, and ERP and carrier integrations.
Part of
4 published case studiesA freight-management platform and mobile apps for a US logistics startup (Mover Technologies)
Freight & Trucking APIs
Design and integration of freight, tracking, and carrier APIs.
Part of
4 published case studiesA freight-management platform and mobile apps for a US logistics startup (Mover Technologies)
CTRM & ETRM
Commodity and energy trading and risk management software, built and integrated.
Part of
1 published case studySoftware for trading with Smart contracts
EV Charging
Charge point management, roaming, and billing for EV charging networks.
Part of
Related serviceCustom software development services
Accounting & Finance
Custom accounting software that streamlines reporting and reconciliation.
Part of
2 published case studiesFour corporate websites for a financial-services group, with accessibility inside the build scope
E-commerce Design
Custom e-commerce storefronts built to convert and grow your brand.
Part of
1 published case studyEcommerce software development for JewelCandle
Nothing here matches that
Most of our work is operational software where reliability and integration are the hard part, and that carries across domains. Clear the search to see all of them, or describe the domain and a senior engineer will map it against our work.
Two weeks, fixed fee, and a written answer
Most operational software is a reliability and integration problem before it is a domain problem. A fixed-scope assessment says where AI and automation pay off in your operation, and names any specialist input your domain calls for.
02Start here
Find your situation, and we will tell you where to start
Five situations, and the right first step for each. Every row routes you to the page or engagement that fits, from a sector page or a platform build to a fixed-scope assessment or a takeover audit, so the first call starts from where your operation is.
| Your situation | What you are deciding | Where to start, and what we would say |
|---|---|---|
| Your sector is on the list | You run an operation in one of the sectors above, and software is the problem. | That industry page. It names the systems and the standards involved, so the first call is about your operation.Back to the directoryOr book a meeting |
| You know the system by name | You know what you need: a WMS, a CTRM, an OCPP charge-point platform, a logistics ERP. | The platform-build page, not the vertical. They exist as their own pages because clients ask for them by name.See the platform buildsOr book a meeting |
| Your sector is not listed | Your domain is not above, and the hard part is reliability or integration. | Neither. Start with a fixed-scope assessment: two weeks, fixed fee, ending in a written plan.See the AI Readiness AssessmentOr book a meeting |
| You need an accredited partner | Your sector needs a clinical, legal or otherwise accredited partner. | We work as the engineering team beside your accredited partner. What we hold is ISO 27001:2022 and ISO 9001:2015, and we build to HIPAA Security Rules and under GDPR.See what we holdOr book a meeting |
| Your system already works | You have a running platform and a team, and the question is whether to bring anyone in. | A short audit first. A takeover opens with a written read of the platform, so you know where outside engineers add value before anyone joins.How a takeover startsOr book a meeting |
03Depth
What industry depth actually buys you
Our domain experience is built to be checked, in three parts: which integrations we have already connected and therefore estimate rather than guess, what the security posture is certified against and by whom, and which published work sits behind each sector, named on that sector's own page.
- The integration surface is already mappedEDI and carrier APIs, channel managers, HL7 and FHIR, OCPP and OCPI, MLS and RETS. Where we have connected a system before, the effort is estimated from that rather than guessed.
- A posture that passes vendor reviewISO 27001:2022 and ISO 9001:2015, both renewed through a multi-stage audit with Quay Audit UK, and ISTQB-certified QA. Contracts and NDAs are signed before anyone starts, and we answer security questionnaires directly.
- The published work, named per sectorEach industry page names the published work behind it, from the energy and utilities trading build to four logistics platforms, and the first call maps your sector to the closest delivered work.
04Case studies
Industry work running in production
Three builds in three of the sectors above, each card ending on the figure the client measured. Every study names the systems behind it.
See all case studies HospitalityHighly Adjustable Platform for entertainment industriesunicrew developed a platform for Booked It that enhanced the customer experience for nightclub, entertainment center, and festival goers.600+Businesses using the platform
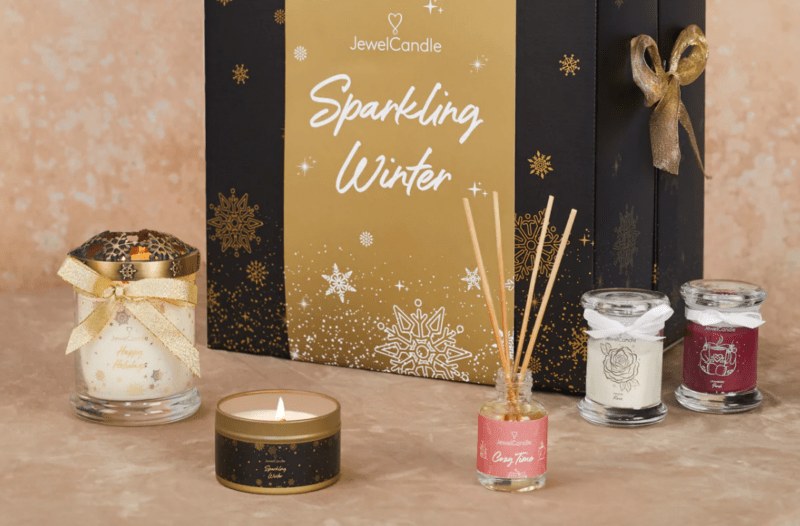 eCommerceEcommerce software development for JewelCandleJewelCandle, a mid-size European manufacturer of scented products, sells across seven EU countries (B2B and B2C) via online shops.10,000-plusProducts manufactured
05Credentials
Certified, audited, and proven
Expertise you can verify: ISO 27001:2022 and ISO 9001:2015 certification (renewed through a multi-stage audit with Quay Audit UK), ISTQB-backed QA in every sprint, a certified Laravel partnership, and named credentials held by the engineers on your team.
Company certifications
 ISO 27001:2022Information security management system, independently audited and renewed through a multi-stage audit with Quay Audit UK.
 ISO 9001:2015Quality management system covering the delivery process, certified in the same audit.
 ISTQBCertified testers on QA, working inside the sprint rather than in a phase bolted on at the end.
 Laravel PartnerOfficially certified Laravel partner company.
Team credentials
 PMIPMP-certified delivery and project leadership, and PMP among the business analysts' certifications.
 Zend PHPZend Certified Engineers on the PHP and Laravel teams.
 Microsoft MCSAMicrosoft Certified Solutions Associate, Web Applications.
 IIBA ECBACertified business analysis for discovery and scoping.
06Client voices
What clients say about the work
We’re one of unicrew’s smaller clients, but they’re always incredibly quick to respond. When we have issues, they treat them as if they’re extremely important. We feel like we have a partner, and that’s been incredible. That’s why we’ll keep them on for as long as we can.
I’ve been impressed by their work ethic and how they put me as the customer first. They’re always ready to jump in and go the extra mile. They put great effort into communicating to ensure that tasks are updated in a timely manner. The team keeps us apprised of exactly what they’re working on.
We had a great experience in working with unicrew and their team: very professional and knowledgable, ready to go the extramile in order to deliver high-quality products. They provided great advices on the best technology solutions to adopt (including blockchain) and were ready to go the extra mile in supporting the client at 360 degrees.
Even though Artelogic didn’t have a background in this area, they learned quickly and repurposed technologies they’d used before in order to solve the business problem. I was very impressed with this ability, as most of the people we contacted before implied that they’d need to spend a lot of time of trying to understand our business logic.
Our platform has been refactored to Laravel ensuring the code base is more stable, easier to maintain and easier to add new features. Their professionalism and quality of work have stood out in the partnership. We have had the code audited by a 3rd party who was extremely complimentary of the work.
07Questions
Industry questions we get on the first call
Answered the way we would answer them live: short, specific, and with the detail you need to plan the next step.
9: transportation and logistics, hospitality and travel, financial services and fintech, healthcare, retail and e-commerce, energy and utilities, automotive, real estate and proptech, and education. Each has a page naming the systems, integrations and standards involved. A further 7 pages cover specialized platform builds inside those industries: logistics ERP, warehouse management, freight and trucking APIs, CTRM and ETRM, EV charging, accounting and finance, and e-commerce design.
Three things you can check for yourself. The integration surface is already mapped, from EDI and carrier APIs to channel managers, HL7 and FHIR, OCPP and OCPI, and MLS and RETS, so effort on a system we have connected before is estimated rather than guessed. The security posture is certified rather than promised: ISO 27001:2022 and ISO 9001:2015, both renewed through a multi-stage audit with Quay Audit UK, with ISTQB-certified QA, and contracts and NDAs signed before anyone starts. And every sector page names the published work behind it.
Yes, when reliability, integration depth or applied AI is the hard part of the problem, which covers most operational software. The quickest way to find out is a call with a senior engineer, or the two-week AI Readiness Assessment, which is fixed-fee and ends in a written plan. Where a domain also needs a regulatory or clinical partner, we plan the engineering around that partner from the first call.
It mostly removes discovery and rework. Requirements gathering is shorter where the questions are already known, and integration effort is estimated from systems we have connected before. Most engagements start within two to four weeks of signature, and there are three billing models: time and materials, billed hourly and quoted per project; fixed price, billed against an agreed outcome; and team extension, billed monthly per team member.
unicrew holds ISO/IEC 27001:2022 for information security and ISO 9001:2015 for quality management, both renewed through a multi-stage audit with Quay Audit UK, and QA is ISTQB-backed. We build healthcare software in accordance with HIPAA Security Rules and handle EU personal data under GDPR. We sign an NDA before anything sensitive changes hands, and we answer enterprise security questionnaires and vendor reviews directly.
Yes. Takeovers are routine work here. The first weeks are a code and infrastructure audit: dependency and CVE review, test coverage, the build and deploy pipeline, and a prioritized list of risks. We stabilize before adding features. For one home-health monitoring platform we took over, we updated the cloud infrastructure, added monitoring, cut AWS operating costs, and stayed on as the client's long-term technology partner. Where a rebuild serves the platform better than continuing, the audit says so in writing.
Published work includes a HIPAA-compliant healthcare application, accounting software integration and automation for a financial advisory company, and an end-to-end SaaS platform for a US moving company. Every industry page lists the studies behind it, the directory above leads with our three priority sectors and orders the rest by published work, and the full index is filterable. For your exact sub-sector, ask on the first call and we will name the closest published analogue and the parts that transfer.
You do. You own the code, the integrations and the data; on an AI build you own the pipeline, the prompts and the data. The pipelines live in your repositories, the infrastructure code sits in your cloud accounts, and the tooling runs on your licences and your billing, so nothing is hostage to the engagement. Once contractual obligations are fulfilled, full ownership of all intellectual property, source code and technical documentation transfers to your organization, and we put that legal framework in place at the start of the engagement rather than at the end.
Where to go next
What we do, in any industry: 36 pages across seven groups.
Fixed-scope engagements that end in a written deliverable.
The stack our engineers ship in production, layer by layer.
Every published project, filterable by the industry behind it.
A build partner on your brand and timeline, across software and AI.
The company, the certifications and the people who deliver.
Tell us how your operation actually works
Thirty minutes with a senior engineer. You get a straight read on what to build first, what to integrate, and what to leave as it is, before anyone writes a proposal.