
Docker consulting services for repeatable releases
We build Docker images and release pipelines for engineering and DevOps teams. We package existing applications for the target runtime, with configuration, state and handover planned as part of the delivery.
01Capabilities
Docker containerization from image to release
Our Docker containerization work connects image design with DevOps consulting. We scope the build, release and runtime requirements together for applications such as hospitality platforms.
- Packaging
Define the image and the state it needs
We pin the selected base image by digest and define a refresh and rebuild policy. The runtime image contains the application dependencies, with build tooling, configuration and secrets kept separate. Persistent state has an explicit home.
- Pipeline
Build, scan and promote the tested artifact
We build and scan the image, then tag and promote the artifact that passed testing. The pipeline runs in Azure DevOps, GitHub Actions or your existing tools, with release and rollback steps defined for the application.
- Parity
Define Docker Compose for development and test
Docker Compose services and seeded data define the dependency versions the application needs. We check the runtime, OS and processor architecture as part of that configuration, so development and test environments have an explicit setup to reproduce.
- Runtime
Choose the production runtime and its owner
We match the images to a managed container service or an assessed cluster, with monitoring and operating responsibilities in scope. The hosting design sits within cloud infrastructure work.
02Case studies
A hotel booking platform migrated with Docker
We migrated a hotel booking platform to Azure using Docker, Microsoft Orleans and Terraform. The move brought lower infrastructure costs and faster transactions.
See all case studies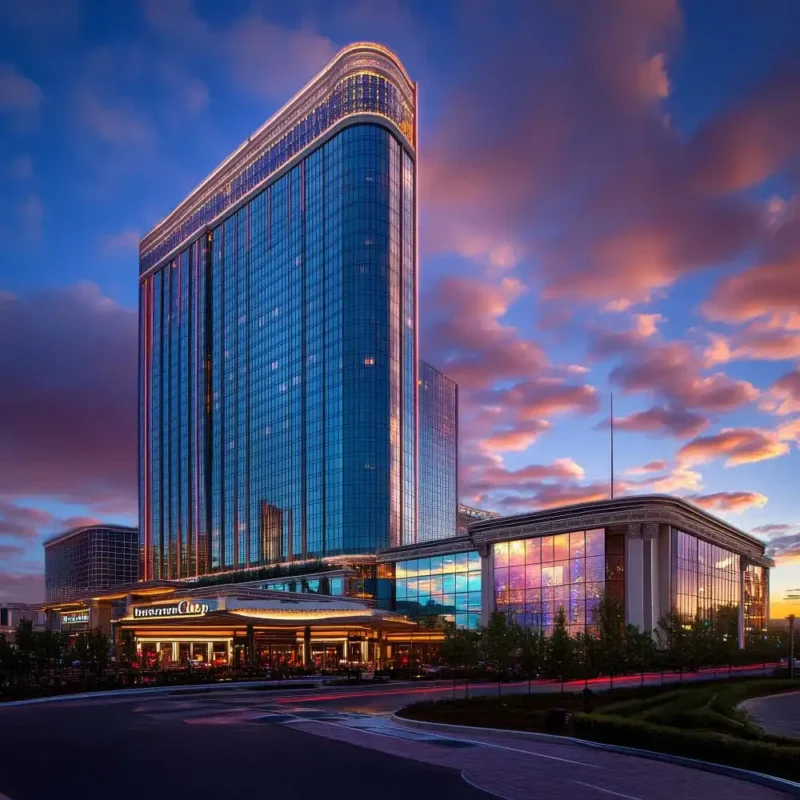
03Fit
Choose packaging, delivery and orchestration separately
Docker packages the application into an image. We assess the release process and target runtime separately, then choose the container, pipeline and hosting work that fits your system.
| Your situation | What we recommend |
|---|---|
| Several services, more than one environment, and deployments that behave differently between them | Use DockerWe define the application image and environment configuration, then verify behaviour on the target runtime. The release promotes the tested artifact. |
| Scheduling, scaling and self-healing across hosts are required | Assess orchestrationWe compare a managed container service with a cluster. Kubernetes covers the orchestration and platform ownership required beyond the application image. |
| One small application, one environment and an established release process | Retain the deployment pathWe scope the release work around the existing deployment path. Containerization is assessed against runtime requirements and the value of a reusable artifact. |
| A manual release process is the main source of delay | Automate releasesWe scope build, verification and release automation through Azure DevOps or your existing tools. Docker packaging is a separate decision within that delivery path. |
| A Windows desktop application depends on specific hardware or an interactive screen | Build an installerWe assess the application and hardware dependencies, then scope a repeatable build and installer for the target environment. |
| A database is part of the production platform | Assess a managed databaseWe compare managed hosting with a containerized database against backup, restore, failover and upgrade responsibilities. Persistent storage and recovery have their own operating scope. |
Scope
We agree the image contents and delivery path, including how configuration and persistent data reach the running container. Handover covers rebuilding, releasing and recovering the application. unicrew has 100+ senior in-house engineers across six countries. We work under an ISO 27001:2022 certified information-security management system.
Docker makes an application run the same way in every environment. Most of the security work is knowing what is inside the image. We start from a pinned base image chosen on purpose, include only what the application uses, and scan it in the pipeline.
 Ihor PrudyvusDelivery Director, unicrew
04Delivery
Containerize the application from inventory to handover
We plan the move to Docker images around the application's current release path.
- Map configuration and persistent stateWe inventory local files, uploaded assets and scheduled jobs alongside certificates and environment variables. Each dependency gets an explicit place in the image, deployment configuration or persistent storage.
- Build and harden the runtime imageWe use a multi-stage Dockerfile to separate compilation and test tools from the runtime image. Digest pins are paired with dependency refresh and rebuild plans; non-root execution, external secrets and health checks are part of the image review.
- Compare behaviour and rehearse cutoverWe run the containerized application alongside the current version against representative traffic and compare the agreed behaviour. The existing release path stays available while we rehearse rollback and prepare cutover.
- Hand over the pipeline and operating runbookWe hand over registry access, image tagging and rollback procedures, including how to inspect a running container. The runbook names who refreshes dependencies and rebuilds the image when vulnerabilities are published.
05Stack
The pipeline and runtime around the image
Choose the build and hosting tools around the Docker image and the platform you already operate.

06Questions
Questions about Docker packaging and operations
Docker packaging and ongoing operations need distinct scopes before the work is quoted.
Yes. We scope Docker engineering around your application package, release pipeline and production runtime.
We agree verification through our QA and test automation practice. A managed development team includes unicrew delivery coordination. When you want us to own the delivery outcome, we scope it through DevOps consulting.
No. Docker packaging and orchestration are separate decisions.
Kubernetes handles scheduling and orchestration across hosts. We assess that platform against a managed container service, including the runtime and configuration requirements and the operational work each option needs.
Yes, where the runtime and platform dependencies support it. We assess the application's state before defining the containerization scope.
The assessment covers:
- filesystem writes and uploaded assets;
- hardcoded paths, hostnames and runtime dependencies;
- crontab jobs and configuration on the current server.
Application changes revealed by the assessment are scoped through modernization.
We use containers for development dependencies and assess production database hosting separately.
Docker Compose and seeded data define the development database. For production, we compare managed hosting with a containerized database against the operating requirements:
- persistent storage and backups;
- restore testing and failover;
- database version upgrades.
We start with an engineering review of the application and its current build and release path.
For an existing system, we ask for read access to the repository and a description of deployment. You get a written recommendation on the container scope, the order of work and the operating responsibilities. Most engagements start within two to four weeks.
Docker work is quoted against the packaging and delivery scope.
- Time and materials is billed hourly and quoted per project.
- Fixed price is outcome based and quoted per project.
- Team extension is billed monthly per team member.
The estimate includes application packaging and the agreed pipeline, verification and handover work.
Scope the container work in your next release
Bring the repository and current release process to a scoping call. We will outline the image design, release pipeline and operating scope within DevOps consulting.